
Enterprise Risk Management in Nigeria: Why Your Company Cannot Afford to Ignore ERM in 2026
Risk is everywhere in Nigeria right now.
The naira moves against the dollar daily. Inflation eats into profits. Regulators demand more. Cybercriminals attack constantly.
Old-style risk management does not work anymore. Keeping risks in separate silos. Finance handles currency risk. IT handles cyber. Operations handles the supply chain. No one talks to anyone else.
Enterprise Risk Management changes that. It looks at everything together. It connects risk to strategy. It protects your business.
Let me explain why ERM matters for Nigerian companies in 2026.
At Stonehill Research , we help organisations build ERM frameworks that work. Our ERM Framework Design and Implementation service is where smart companies start.
What is Enterprise Risk Management? Let me explain
The most widely cited definition comes from COSO. According to COSO, Enterprise Risk Management is: “A process, effected by an entity’s board of directors, management and other personnel, applied in strategy setting and across the enterprise, designed to identify potential events that may affect the entity, and manage risk to be within its risk appetite, to provide reasonable assurance regarding the achievement of entity objectives.”
That was formal. Sorry.
Here is the real talk. ERM moves beyond siloed, department-by-department risk management. It integrates risk identification, assessment, and response into your overall strategy. It creates a unified, holistic view of risk across every function from finance and operations to compliance and technology.
Think of it like a central nervous system for risk. Your left hand knows what your right hand is doing. And your brain coordinates everything.
Why ERM is critical for Nigerian companies
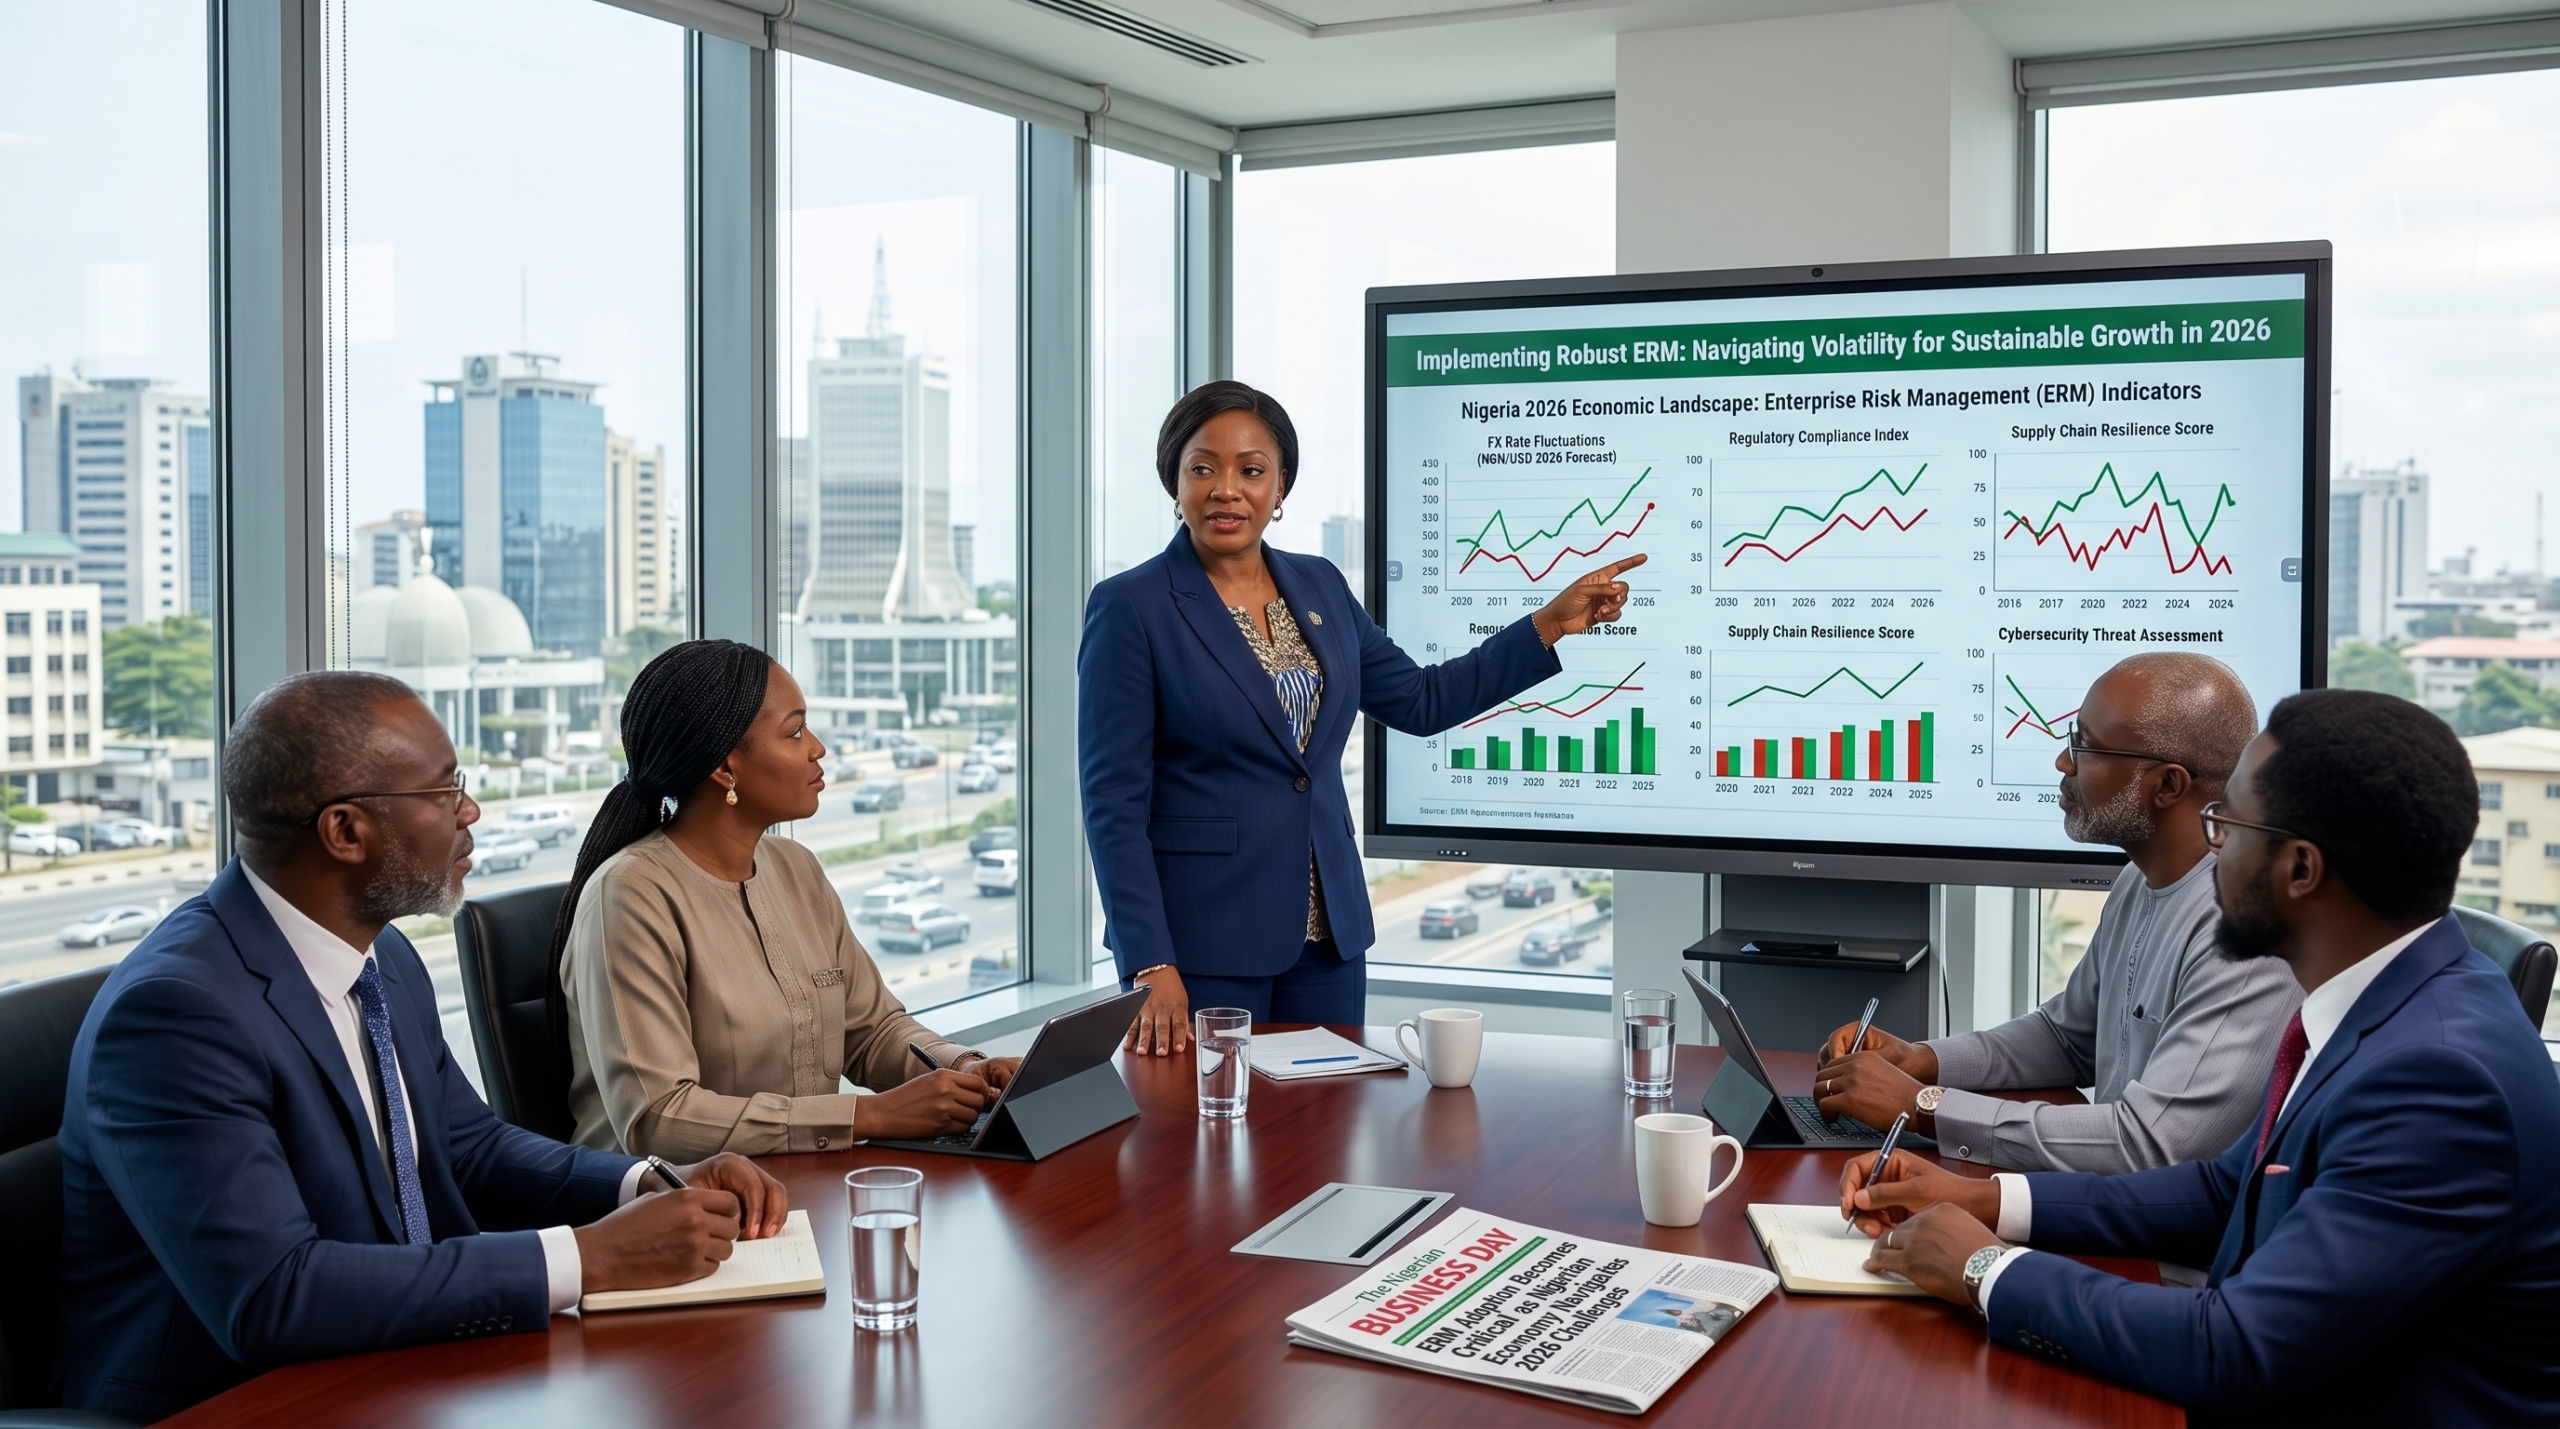
Nigeria’s business environment has grown significantly more complex in recent years. Macroeconomic volatility, persistent foreign exchange challenges, high inflation, and rising cybersecurity threats have made risk management a boardroom priority.
Regulators now demand clear evidence of formal, enterprise-wide risk management systems.
According to a February 2026 report by Kreston Pedabo, regulators are no longer willing to accept fragmented or informal risk practices. Organisations are expected to demonstrate that ERM frameworks are fully integrated into governance structures and everyday decision-making. Not policies that exist only on paper.
For Nigerian businesses, the consequences of inadequate risk management extend well beyond regulatory sanctions. Financial losses. Reputational damage. Loss of investor confidence. Business failure.
Companies that invest in robust ERM frameworks are better positioned to anticipate risks, seize opportunities, and maintain stakeholder trust.
The Nigerian regulatory landscape
Securities and Exchange Commission (SEC) – Mandatory ERM for Capital Market Operators.
In June 2024, the SEC issued a directive requiring all Capital Market Operators to implement an ERM framework conforming to international standards, including COSO ERM, ISO 31000, and FATF Recommendations. Every CMO must establish a risk governance structure with clearly defined roles, submit an annual Risk Profile to the Commission by January 31 each year, and report emerging threats whenever significant business changes occur.
Central Bank of Nigeria (CBN) – Risk-Based Supervision and Bank Recapitalisation.
The CBN has adopted a risk-based supervision model, placing direct responsibility for risk oversight on boards and senior management. Banks must maintain comprehensive ERM frameworks covering credit, market, liquidity, operational, and cyber risks.
The CBN’s bank recapitalisation exercise, concluding in March 2026, has pushed banks to raise minimum capital to ₦500 billion for international banks, ₦200 billion for national banks, and ₦50 billion for regional banks. This directly intersects with ERM governance requirements.
Investments and Securities Act 2025.
President Bola Tinubu assented to the Investments and Securities Act 2025, which repeals the ISA 2007 and introduces updated governance and risk management expectations for all capital market participants. The Act strengthens the SEC’s oversight powers and elevates enterprise-wide risk management as a core element of good corporate governance.
The role of AERMP in professionalising ERM in Nigeria.
The Association of Enterprise Risk Management Professionals (AERMP) is the foremost professional body for risk management practice in Nigeria. It is an independent, not-for-profit institute duly registered and approved by the Federal Government to set professional standards in enterprise risk management practice across all industries and sectors.
AERMP maintains strategic partnerships with the Institute of Risk Management in the UK and the Fred Arditti Centre for Risk Management at De Paul University in the USA. The body has been invited to the Presidential Villa by the Federal Government to contribute to managing cybersecurity risk in Nigeria.
For Nigerian risk professionals, AERMP qualifications and membership are becoming increasingly valuable as regulators entrench ERM practices across financial and non-financial sectors.
The Kreston Pedabo DAPM ERM Framework.
In early 2026, Kreston Pedabo introduced the DAPM ERM Framework, a scalable model designed specifically for Nigerian organisations. It operates across four stages. Discover means identifying and profiling risks. Analyse means prioritising through heat maps and scenario analysis. Protect means designing targeted controls. Monitor means continuous oversight through key risk indicators and board-level reporting.
Key components of an effective ERM framework
Whether guided by COSO ERM 2017 or ISO 31000, all effective ERM frameworks share common structural components. For Nigerian companies, these must be tailored to the local operating environment while meeting international standards.
Risk governance structure. The board of directors must take ownership of risk oversight. A dedicated Risk Management Committee or Audit and Risk Committee should have clearly defined terms of reference. Regulatory expectations across CBN, SEC, and NAICOM all emphasise board accountability as a non-negotiable baseline.
Risk appetite and risk tolerance. Every organisation must define how much risk it is willing to accept in pursuit of its strategic objectives. It must also set specific thresholds that guide risk-taking behaviour. These statements must be board-approved, clearly documented, and communicated throughout the organisation.
Risk identification and assessment. A systematic process must identify risks across all categories. Strategic, financial, operational, compliance, reputational, and emerging risks, such as cybersecurity and AI-related threats. Identified risks should be assessed for likelihood and potential impact, then prioritised using tools like risk heat maps and scenario analysis.
Risk response strategies. For each significant risk, management must determine the appropriate response. Avoidance, reduction, sharing, or acceptance. This links directly to the organisation’s strategic decision-making processes.
Internal controls and monitoring. Robust internal controls are the operational backbone of ERM. Continuous monitoring through key risk indicators, management dashboards, and internal audit reviews ensures the ERM framework remains active and responsive.
Risk culture. No ERM framework can succeed without a strong risk culture. This means fostering an environment where every employee understands risk, feels empowered to raise concerns, and incorporates risk thinking into daily decisions. Visible commitment from the board and executive management is essential.
Major business risks facing Nigerian companies in 2026
Understanding the specific risk landscape is essential for designing a relevant and effective ERM framework.
Macroeconomic and foreign exchange risk. Nigeria’s economy continues to face foreign exchange pressures, high inflation, and interest rate volatility. These directly affect revenue, cost of goods, import costs, debt servicing, and investor returns. Companies without formal FX risk management embedded in their ERM frameworks remain highly exposed.
Regulatory and compliance risk. The rapid pace of regulatory change across the CBN, SEC, NAICOM, FRC, and the new Nigeria Tax Act 2025 creates significant compliance risks. Organisations that are not proactively monitoring regulatory developments will fall behind.
Cybersecurity and digital risk. Cyber threats represent one of the fastest-growing risk categories in Nigeria. As businesses digitalise, the attack surface for cybercriminals expands. The CBN’s Risk-Based Cyber Security Framework makes cybersecurity risk management a regulatory requirement for financial institutions.
AI and technology risk. The Kreston Pedabo report specifically flagged AI-related risks, including data privacy, algorithmic bias, transparency, ethical use, and third-party reliance as an emerging priority. In the absence of dedicated AI regulation, boards must explicitly integrate AI risks into existing governance and data protection structures.
ESG and sustainability risk. ESG expectations are rising among investors, lenders, and development finance institutions. For Nigerian companies seeking foreign investment or accessing development finance, demonstrating credible ESG risk management is increasingly a prerequisite.
Operational and reputational risk. Supply chain disruptions, power infrastructure challenges, logistics complexities, and talent retention issues remain persistent operational risks. Reputational risks, amplified by social media, can spread rapidly and cause lasting brand damage.
Read our article on How to Build a Risk Register That Your Board Will Actually Read for practical guidance on documenting your risk landscape.
Practical steps to implement ERM in your Nigerian organisation
Step one: Secure board and executive commitment.
ERM implementation begins at the top. The board must formally endorse ERM as a strategic priority. Allocate adequate resources. Establish the risk governance structure. Without visible leadership commitment, ERM efforts will struggle.
Step two: Select and adopt a recognised framework.
Choose an internationally recognised ERM framework appropriate to your sector and size. The COSO ERM Framework (2017 edition) and ISO 31000:2018 are the most widely used. Both are accepted by Nigerian regulators. Formally document the framework selection and communicate it to stakeholders.
Step three: Conduct an enterprise-wide risk assessment.
Facilitate structured risk identification workshops across all business units. Use interviews, surveys, and data analysis to surface risks across all categories. Develop a comprehensive risk register and risk heat map that gives leadership a clear, prioritised view of the organisation’s risk landscape.
Step four: Define risk appetite and establish risk limits.
Work with the board to articulate a formal risk appetite statement. Define specific risk tolerance limits for major risk categories. Embed these into decision-making processes, investment approvals, and operational policies.
Step five: Design and implement risk responses and controls.
For each prioritised risk, define the appropriate response strategy. Design specific controls or action plans. Assign clear ownership to a named individual or team, with accountability for implementation and reporting.
Step six: Build a continuous monitoring and reporting system.
Establish key risk indicators that provide early warning signals when risks approach tolerance thresholds. Design regular risk reporting to the board, audit committee, and senior management throughout the year.
Step seven: Invest in risk culture and capacity building.
Provide structured ERM training to boards, senior management, and key staff. The Association of Enterprise Risk Management Professionals (AERMP) and the Institute of Risk Management (IRM) Nigeria Group both offer professional development programmes.
Our Board and Executive ERM Training helps leadership teams build risk capability.
The business case for ERM: beyond compliance
Compliance with regulatory requirements is a compelling reason to invest in ERM. But the benefits extend much further.
Better strategic decision-making. When risk information is integrated into strategy setting and performance management, decisions are made with a clearer understanding of uncertainty. This reduces costly surprises and improves strategic outcomes.
Access to capital and investment. Investors, lenders, and development finance institutions are increasingly requiring evidence of formal ERM frameworks before committing capital. Companies with demonstrable ERM maturity are better positioned to attract investment.
Fraud prevention and reduced financial losses. Strong internal controls and risk monitoring are the first line of defence against fraud and financial mismanagement. Prevention costs are always lower than recovery costs.
Operational efficiency. The process of identifying and assessing risks frequently reveals operational inefficiencies and redundancies. When addressed, these improve productivity and reduce costs.
Common ERM implementation challenges in Nigeria
Limited ERM expertise and awareness. A shortage of qualified ERM professionals and limited board-level familiarity with risk management concepts remains a challenge. Address this with intentional investment in training, professional development, and external advisory support. AERMP is actively working to raise professional standards across the country.
ERM is treated as a compliance exercise. Many organisations implement ERM frameworks primarily to satisfy regulators. This results in static documentation that does not inform decision-making. This approach fails to deliver strategic and operational benefits.
Weak risk culture. Where tone from the top is absent or unconvincing, risk awareness fails to permeate the organisation. Employees who do not understand why risk management matters will not contribute to effective ERM.
Inadequate data and information systems. Effective risk monitoring depends on reliable, timely data. Many Nigerian companies lack the information management systems needed to generate meaningful risk indicators.
Resource constraints in smaller companies. For smaller organisations, dedicating adequate resources to ERM is challenging. A proportionate, risk-focused approach prioritising the highest risks and most critical controls is more sustainable.
Where to start tomorrow
Do not try to build a perfect ERM framework overnight.
First, start with a risk assessment. Identify your top ten risks. Understand what keeps you up at night.
Second, secure board commitment. Present the case for ERM. Show them the regulatory requirements.
Third, adopt a framework. COSO ERM or ISO 31000 are both good choices. Pick one and start.
Fourth, build a risk register. Document your risks, assessments, and responses. Keep it live.
Fifth, monitor continuously. Risk changes daily. Your ERM framework must change with it.
Finally, get help if needed. ERM implementation is complex. Professional advisors save time and prevent mistakes.
Recommended reading from the Stonehill Research blog
While you are here, check out these related articles from our team:
-
How to Build a Risk Register That Your Board Will Actually Read – Moving beyond static risk lists
-
ISO 31000 vs COSO ERM: Which Framework Is Right for Your Nigerian Company? – Choosing the right standard for your sector
-
Risk Appetite Statements: What Nigerian Boards Get Wrong – Common pitfalls and how to avoid them
-
Embedding ERM into Strategic Planning: A Practical Guide – Connecting risk to business decisions
Related services from Stonehill Research
We help organisations build risk-resilient businesses. Here is how:
-
Growth Strategy Design – Building strategies that work in Nigeria’s unique environment
-
Market Segmentation – Treating Nigeria as multiple markets, not one
-
Consumer Insight Research – Understanding real needs and behaviours
-
Strategic Alignment Review – Aligning structure with strategy
-
Operational Resilience Assessment – Building systems that absorb friction
-
Talent and Capability Development – Developing talent and institutional knowledge
-
Data-Driven Decision-Making Frameworks – Making better business decisions with data
About Stonehill Research
Stonehill Research helps organisations move from ambition to execution. Our data-driven insights enable businesses, investors, and policymakers to design strategies that reflect Nigeria’s real market conditions.
We understand the complexity. Market fragmentation. Infrastructure gaps. Regulatory volatility. Capital constraints. We have seen it all.
We do not guess. We use market data to guide our recommendations. And we do not just give you a strategy document. We help you execute.
That matters for ERM because risks evolve quickly. You need current, practical frameworks. You need a partner who understands how these risks play out in real Nigerian organisations.
Final word from the trenches
ERM is not optional for Nigerian companies in 2026.
SEC requires it for Capital Market Operators. CBN expects it from banks. NAICOM demands it from insurers. Investors look for it before committing capital.
But beyond compliance, ERM makes your business stronger. Better decisions. Fewer surprises. Stronger investor confidence.
The regulators are watching. Your competitors are implementing ERM. Your stakeholders are asking questions.
Do not wait for a crisis to build your risk framework. Start now.
Stonehill Research is your trusted partner in enterprise risk management. We help you move from ambition to execution.
Let’s work together
Ready to strengthen your ERM framework?
Contact us today:
📧 Email: info@stonehillresearch.com
📞 Phone: +234 802 320 0801
📍 Address: 5, Ishola Bello Close, Off Iyalla Street, Alausa, Ikeja, Lagos, Nigeria
Warri Office:
Suite 7, 2nd Floor, St Elizabeth Plaza, 77, Okumagba Avenue, Warri, Delta State
📞 Matthew: 08023200801 | Fred: 08062532219
Stonehill Research – Your Trusted Partner in Enterprise Risk Management
References
-
Wikipedia. Enterprise Risk Management (COSO Definition). https://en.wikipedia.org/wiki/Enterprise_risk_management
-
Vanguard Nigeria / Kreston Pedabo. Tougher regulation pushing Nigerian firms towards stronger risk management frameworks. https://www.vanguardngr.com/2026/02/tougher-regulation-pushing-nigerian-firms-towards-stronger-risk-management-frameworks-pedabo/
-
BusinessDay Nigeria. Regulation pushes Nigerian firms to boost risk management. https://businessday.ng/news/article/regulation-pushes-nigeria-firms-to-boost-risk-management/
-
Securities and Exchange Commission Nigeria. Circular on the Implementation of Enterprise Risk Management.
-
COSO. Enterprise Risk Management – Integrating with Strategy and Performance. https://www.coso.org/guidance-erm
-
Association of Enterprise Risk Management Professionals Nigeria (AERMP). About Us. https://aermp.org/about/
-
BusinessDay Nigeria. Here are 20 banks that have met the new CBN capital rules.
There are no comments